01 / 06
Deployment that fits policy
Single-tenant SaaS as standard, with on-premises deployment available, the same product and update cadence.
Capex Platform · Security & Governance
Architecture, security and governance for the IT, finance and risk teams responsible for reviewing the platform and operating it over time.
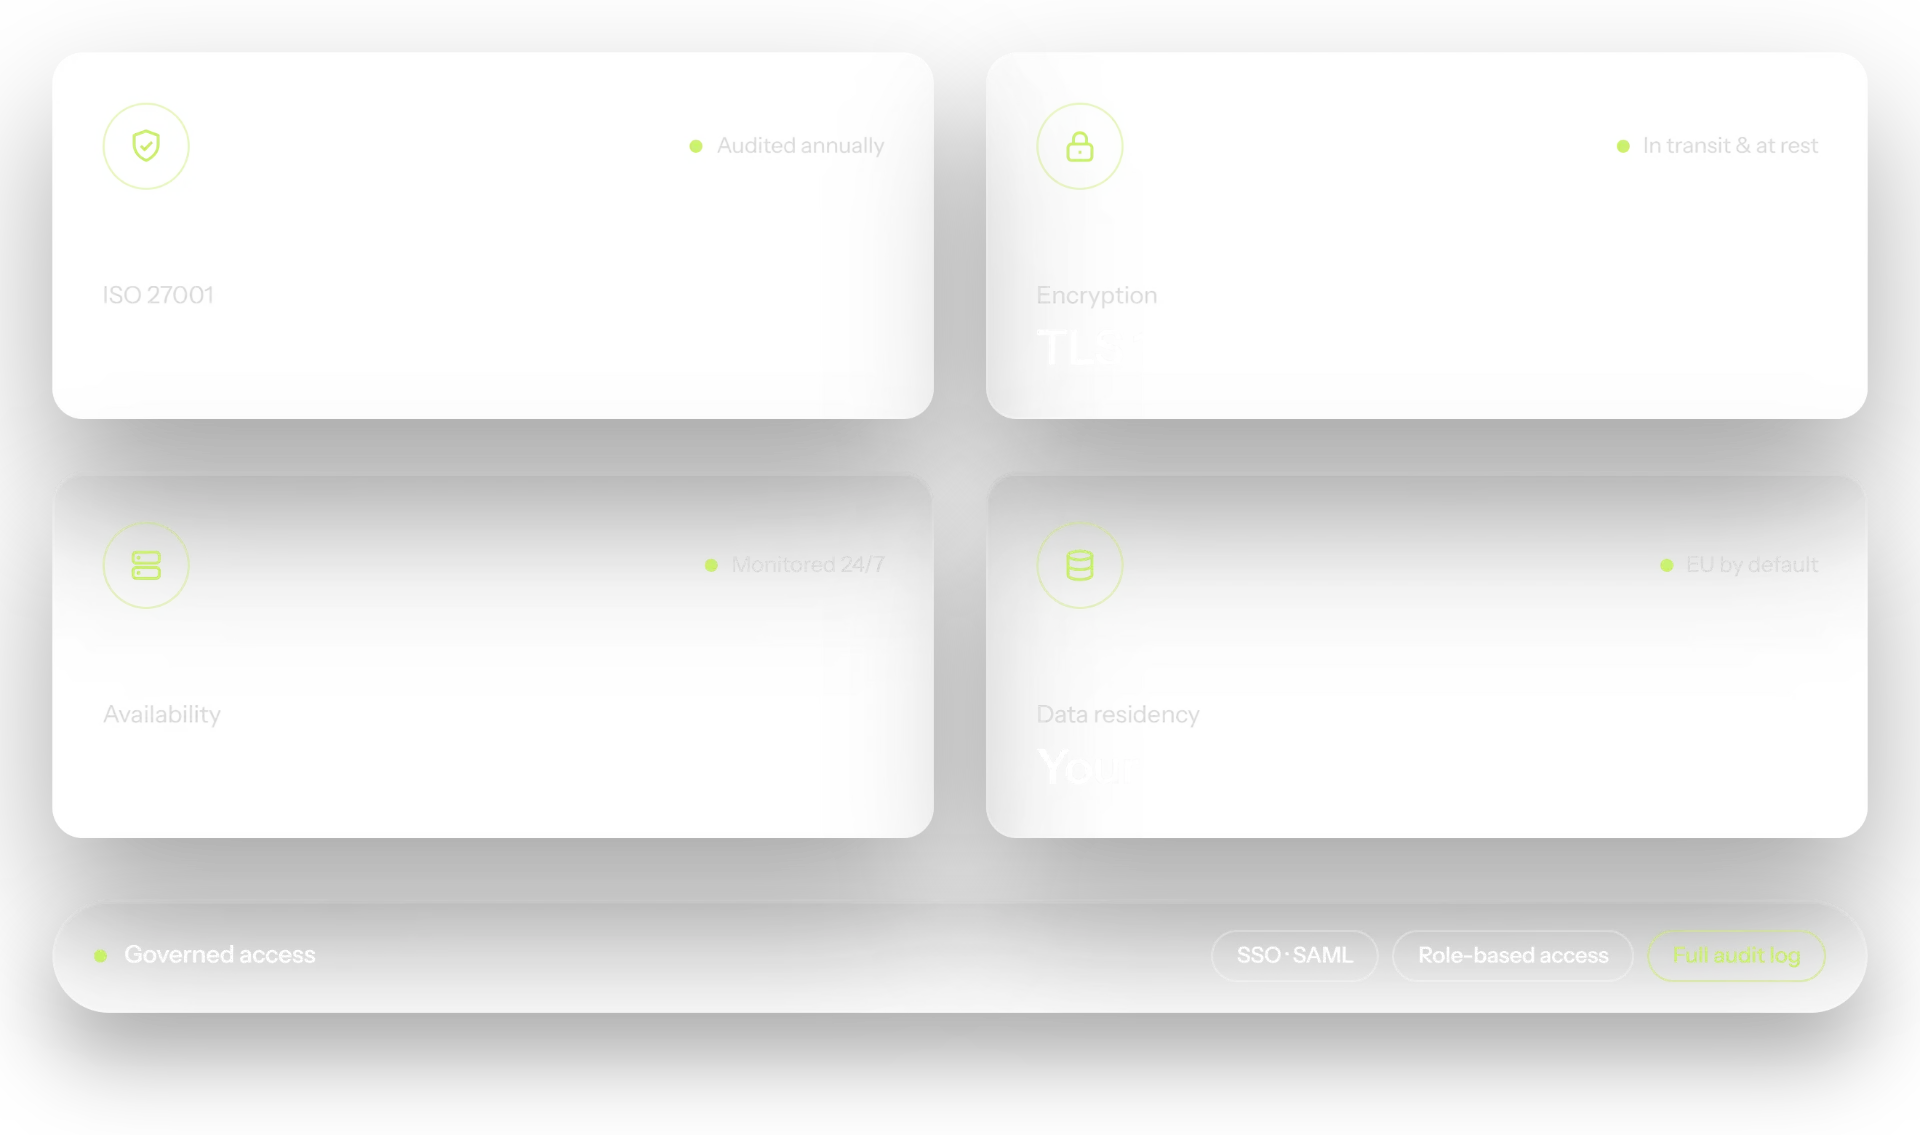
ISO 27001
Certified information security
99.5%
Monthly uptime SLA
RPO 1h
RTO 4h disaster recovery
Global
Regional or on-prem deployment
Architecture
Apply the same identity, deployment and operating standards across sites and legal entities.
Single-tenant SaaS as standard, with on-premises deployment available, the same product and update cadence.
Provision in the required AWS region and keep tenant data and backups inside that region.
Finance configures workflows, forms and routing without routine IT tickets.
SAML 2.0, OIDC, SCIM 2.0 and MFA through leading identity providers.
Capture actor, timestamp and before-and-after values; export records to your SIEM.
Zero-downtime delivery, vulnerability monitoring and a public service status page.
Security & compliance
The certificate is available under NDA together with the supporting security documentation.
Data processing terms, a published sub-processor list and change notification support enterprise privacy reviews.
Tenant data, backups and logs are encrypted. Customer-managed keys are available on the Enterprise tier.
Permissions apply consistently to people, integrations and AI capabilities across the platform.
Independent testing complements continuous scanning, dependency monitoring and severity-based remediation targets.
Encrypted backups span availability zones and disaster-recovery runbooks are tested annually.
AI uses the same access controls as a human user. Customer data is not used to train cross-tenant models.
For every stakeholder
Talk directly with the people responsible for the architecture and security programme.
Book a demo